EkranlarScreens
Log ile kanıt aynı şey değildir. Log ne olduğunu yazar; kanıt, yazılanın sonradan değişmediğini gösterir. Bu sayfa ikincisinin nasıl kurulduğunu anlatır. A log and a piece of evidence are not the same thing. A log says what happened; evidence shows that what was written has not changed since. This page is about the second one.
Her katman farklı bir saldırganı hedefler. İlk üçü kurumun sunucularında çalışır; dördüncüsünü denetçi, kurumun dışarı yazdığı özetlerle kendisi yapar.Each layer targets a different attacker. The first three run on the organisation's servers; the fourth is done by the auditor personally, using the digests the organisation wrote out.
Denetim kayıtları SQL Server 2022'nin append-only ledger tablosunda durur. Veritabanı motoru kayıt değiştirmeyi ve silmeyi herkes için reddeder. Kayıtlar tek bir yordamla yazılır, olay zamanını o yordam verir ve defter her kaydı yazan veritabanı kimliğini kendisi tutar. Ürün, kanıt tablosunda tetikleyici olmadığını ve yazma yordamının değişmediğini varsayılan olarak 15 dakikada bir denetler; bu sınır bozulursa değişiklik işlemlerini durdurur.Audit records live in a SQL Server 2022 append-only ledger table. The database engine refuses updates and deletes for everyone. Records are written through a single procedure, which sets the event time, and the ledger itself keeps the database identity that wrote each record. By default every 15 minutes the product checks that the evidence table has no trigger and that the write procedure has not changed; if that boundary breaks, change operations stop.
Kimi yakalar:Who it catches: kaydı sonradan değiştirmek ya da silmek isteyen herkes, veritabanı yöneticisi dahil.anyone who wants to alter or delete a record afterwards, the database administrator included.
Defter özeti varsayılan olarak saatte bir alınır. Özeti API üretir; imza anahtarı tanımlıysa kurumun RSA anahtarıyla imzalar ve tanımlı çıkış klasörüne, yani kurumun değiştirilemez deposuna (saklama kilitli bir nesne deposu ya da WORM paylaşımı) dosya olarak yazar. Worker yalnız turu başlatır ve imza anahtarına erişmez. Kurulum varsayılanında imza kapalıdır ve klasör tanımlı değildir; bu ayarlar yapılmazsa dış dosya yazılmaz ve Yönetişim Kurulum Kontrolü ekranı bunu gösterir; deponun değiştirilemez olmasını kurum sağlar. Özet dışarıda durduğu için veritabanı yeniden kurulsa bile fark doğrulamada görünür.The ledger digest is taken every hour by default. The API produces it, signs it with the organisation's RSA key where a signing key is configured, and writes it as a file to the configured output folder, the organisation's immutable store (an object store with a retention lock, or a WORM share). The Worker only starts the cycle and has no access to the signing key. At installation signing is off and no folder is configured; until these settings are made no external file is written and the Governance Readiness screen shows it; making the store immutable is the organisation's part. Because the digest sits outside, the difference shows in verification even if the database is rebuilt.
Kimi yakalar:Who it catches: veritabanı dosyasını doğrudan değiştiren ya da eski bir yedeğe dönen kişi.someone who edits the database file directly or rolls back to an older backup.
Ürün tablolarının üzerindeki tetikleyiciler, satır değişikliklerini uygulamadan bağımsız olarak ayrı bir kayda yazar: veritabanı girişi, makine, uygulama adı, eski ve yeni değer. Denetim dosyası, defterle uyuşmayan bir alanı bu kayıtla eşleştirir. Bu katman ipucudur, kanıt değeri defterdedir: tetikleyici kapatılarak yapılan değişiklik burada iz bırakmaz; defterde karşılığı olan alanlarda ise defterle karşılaştırmada görünür.Triggers on the product tables write row changes to a separate record, independently of the application: database login, host, application name, old and new value. The evidence dossier matches a field that disagrees with the ledger against this record. This layer is a lead, the evidential weight is in the ledger: a change made with the trigger disabled leaves no trace here; where the field has a ledger counterpart it still shows in the comparison with the ledger.
Kimi yakalar:Who it catches: uygulamayı baypas edip ürün tablolarını doğrudan değiştiren kişi.someone who bypasses the application and changes the product tables directly.
Denetçi, kurumun kendi ortamında bir yedekten geri yüklenmiş kopyayı SQL Server'ın kendi yordamı sys.sp_verify_database_ledger ile, değiştirilemez depodan aldığı özetlere karşı doğrular. Yedek kurumdan çıkmaz ve SQL Change Guard yazılımı gerekmez.The auditor verifies a copy restored from backup in the organisation's own environment with SQL Server's own procedure, sys.sp_verify_database_ledger, against the digests collected from the immutable store. The backup does not leave the organisation and no SQL Change Guard software is needed.
Kimi yakalar:Who it catches: dış özet alındıktan sonra geçmişi yeniden yazmaya çalışan; doğrulama ürünün ve kurumun söylediğine güvenmeden yapılır. Uygulama hesabıyla yazılmış tutarlı bir olayı bu katman ayırt etmez; ona karşı hedefteki bağımsız izleme gerekir.anyone who rewrites history after a digest has been written outside; the verification does not rely on what the product or the organisation says. It does not tell apart a consistent event written with the application account; that needs independent monitoring on the target.
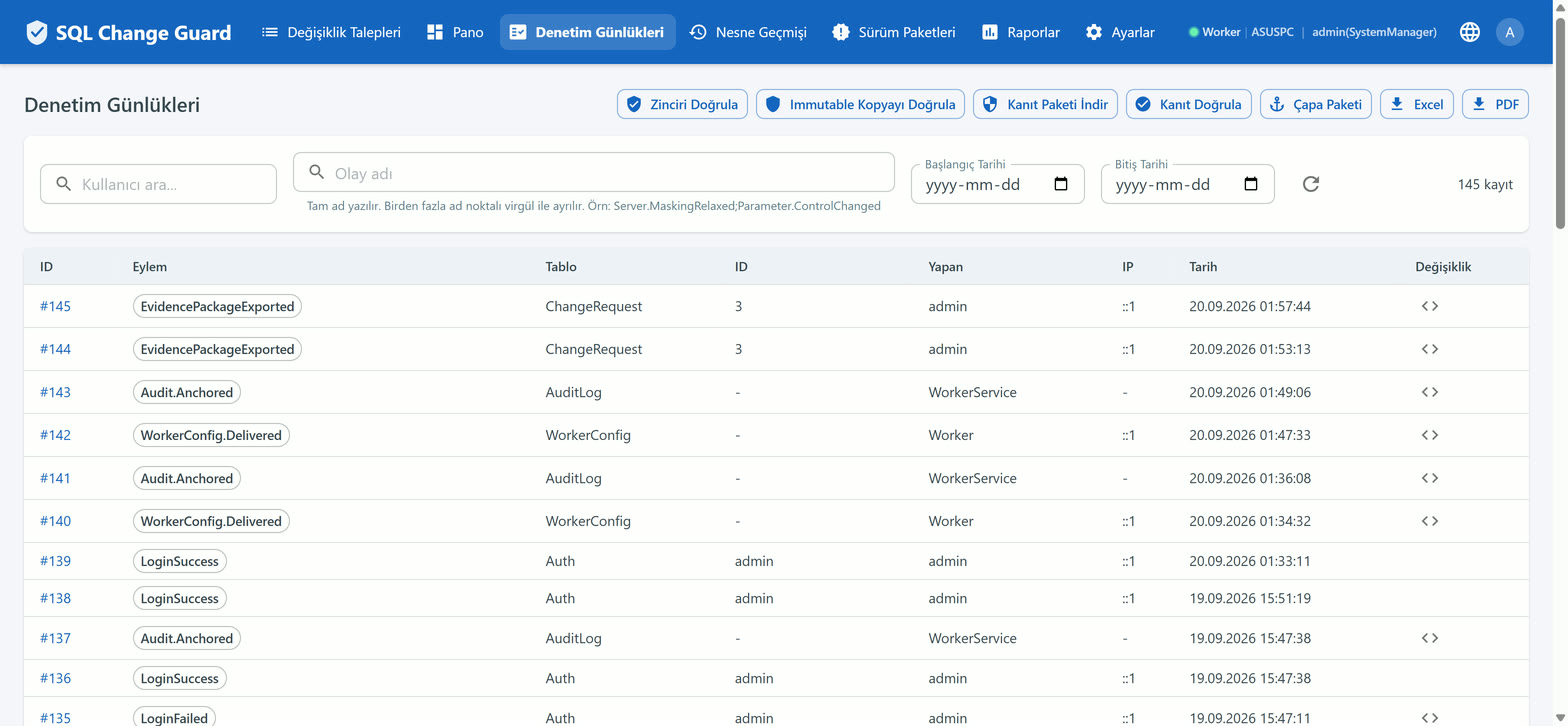
Denetim ekranında ne var. Defter Durumu düğmesi kanıt tablosunun gerçekten append-only defter olduğunu, yazma sınırını, son defter özetini ve dış depoyu gösterir. Kanıt Doğrula, elinizdeki bir paketin bu kurulumdan çıkıp çıkmadığını söyler. Dönem paketi ve kayıt paketi de buradan indirilir. Bunlar ürünün kendi görüşüdür; bağımsız doğrulama denetçinin kendi makinesinde yapılır: kanıtı kendiniz nasıl doğrularsınız.What the audit screen offers. The Ledger Status button shows whether the evidence table really is an append-only ledger, the write boundary, the latest ledger digest and the external store. Verify Evidence tells you whether a package in your hand came out of this installation. The period package and the records package are downloaded here as well. These are the product's own view; independent verification happens on the auditor's own machine: how you verify the evidence yourself.
Denetim genellikle şöyle ilerler: denetçi rastgele bir değişiklik seçer ve o değişikliğin hikâyesini ister. Kim istedi, hangi kurala göre onaylandı, kim çalıştırdı, betik o gün ne idi.
An audit usually goes like this: the auditor picks a change at random and asks for its story. Who asked for it, under which rule it was approved, who ran it, what the script was on the day.
Bu sorunun cevabı tek bir dosya olarak dışa aktarılır. İçinde künye, görevler ayrılığı ve o gün geçerli kurallar, zaman çizelgesi, onay kanıtı, betiğin parmak izi, risk dökümü, izole deneme sonucu, çalıştırma sonucu, ITSM kontrolleri, kararı verenlerin oturum bilgisi, sorgu teslim bilgisi, istisnalar ve ham denetim izi bulunur.
The answer exports as a single file. It carries the identity block, separation of duties and the rules in effect that day, the timeline, the approval evidence, the script fingerprint, the risk breakdown, the sandbox result, the execution result, the ITSM checks, the session details of the decision makers, query delivery metadata, exceptions and the raw audit trail.
Dosyadaki bilgilerin bir kısmı ürünün normal tablolarından okunur. Dosya üretilirken bu bilgilerin her biri defterdeki haliyle alan alan karşılaştırılır ve sonuç dosyada ayrı bir bölüm olarak yazar: PASS, MISMATCH, MISSING, UNEXPECTED ya da INTEGRITY_FAILURE. Ayrıca her olayın zamanı defterdeki commit zamanıyla, yazan kimlik de ürünün kendi hesaplarıyla karşılaştırılır. Uyuşmayan bir şey varsa dosyanın en üstündeki hüküm kırmızıdır. Bu hüküm ürünün kendi değerlendirmesidir; bağımsız doğrulama denetçinin elindedir.
Part of the information in the file is read from the product's regular tables. While the file is produced, each item is compared field by field with its state in the ledger, and the result is written as a separate section: PASS, MISMATCH, MISSING, UNEXPECTED or INTEGRITY_FAILURE. The time of every event is also compared with its commit time in the ledger, and the writing identity with the product's own accounts. If anything disagrees, the verdict at the top of the file is red. That verdict is the product's own assessment; independent verification stays with the auditor.
Dosyanın kendi mührü vardır ve bu mühür denetim kaydına da yazılır. Dosyanın üretimden sonra değiştirilip değiştirilmediği bu iki değerin karşılaştırılmasıyla anlaşılır.
The file carries its own seal, and that seal is also written into the audit record. Comparing the two is how you tell whether the file changed after it was produced.
Teslim edilen şey tek bir zip dosyasıdır. İçinde verinin yanında bir künye dosyası ve bir doğrulama betiği, imza anahtarı tanımlı kurulumda ayrıca o künyenin RSA imzası ve imzayı doğrulayan açık anahtar bulunur. Denetçi bu doğrulamayı ürüne hiç bağlanmadan, kendi makinesinde yapabilir: kanıt paketi nasıl doğrulanır.
What is delivered is a single zip. Alongside the data it holds an identity file and a verification script and, where a signing key is configured, the RSA signature over that file and the public key that checks the signature. The auditor can run that verification on their own machine without ever connecting to the product: how an evidence package is verified.
İki kural. Sorgu talebinde sonucun kendisi dosyaya girmez; yalnız kime teslim edildiği ve hangi kolonun maskesiz onaylandığı yazılır, aksi halde dosya yeni bir sızıntı kanalı olurdu. İkincisi, dosyanın dışa aktarılması da bir olaydır ve denetim kaydına yazılır. Two rules. For a query request the result itself does not enter the file; only who received it and which column was approved unmasked, otherwise the file would become a new leak channel. Second, exporting the file is itself an event and is written to the audit record.
Örnek, ürünün geliştirme ortamında gerçek bir akışla üretilmiştir ve değiştirilmemiştir. Paketin tamamını (zip) indirip içindeki Verify.ps1 ile kendiniz doğrulayabilirsiniz. The sample was produced by a real flow in the product's development environment and has not been modified. You can download the whole package (zip) and check it yourself with the Verify.ps1 inside.
Bir talep kaydedilirken, onu etkileyen kural seti ve etkin ayarlar tek bir denetim olayında dondurulur. Altı ay sonra kurallar değişmiş olsa bile talebin hangi kurallara göre değerlendirildiği okunabilir.When a request is saved, the rule set and effective settings that shaped it are frozen into a single audit event. Six months later, even if the rules have changed, you can still read which rules the request was judged by.
Bir kuralı kapatmak veya derecesini düşürmek, kural güncellemesi olayıyla (SqlStandard.Update) eski ve yeni değeri birlikte denetim kaydına yazılır ve SIEM'e kontrol değişikliği olarak, ciddiyet eşiğinden bağımsız gider. Ayrı bir olay adı yalnız uygulama yapılandırmasının gevşetilmesinde (App.ControlRelaxed) ve sunucu kontrol alanlarının gevşetilmesinde (örneğin Server.MaskingRelaxed) kullanılır. Böylece "denetimden önce hangi kontroller gevşetildi" sorusu cevaplanabilir.Turning a rule off or lowering its tier is written to the audit record by the rule update event (SqlStandard.Update) with its old and new value, and goes to the SIEM as a control change regardless of the severity threshold. A separate event name is used only when the application configuration is relaxed (App.ControlRelaxed) or a server control field is relaxed (for example Server.MaskingRelaxed). That makes "which controls were relaxed before the audit" an answerable question.
Dört göz açıldığında ayar ekranlarındaki değişiklik canlı kayda hemen yazılmaz; kurum bunu bütün ayarlar ya da yalnız kontrol ayarları için açar, kurulum varsayılanında kapalıdır. Bekleyen bir kayıt olarak durur ve başka bir kullanıcının onayını bekler. Kendi talebini onaylamak her zaman yasaktır.With four eyes switched on, a change on a settings screen is not written to the live record straight away; you switch it on for all settings or for control settings only, and it is off at installation. It waits as a pending entry for another user to approve. Approving your own request is always forbidden.
Talep sahibinin kendi talebini çalıştırması gibi durumlar dosyada istisna olarak görünür. Yönetişimin ölçüsü ihlalin hiç olmaması değil, olduğunda görünmesidir.Cases such as a requester executing their own request appear in the file as exceptions. Governance is not measured by the absence of violations but by whether they surface.
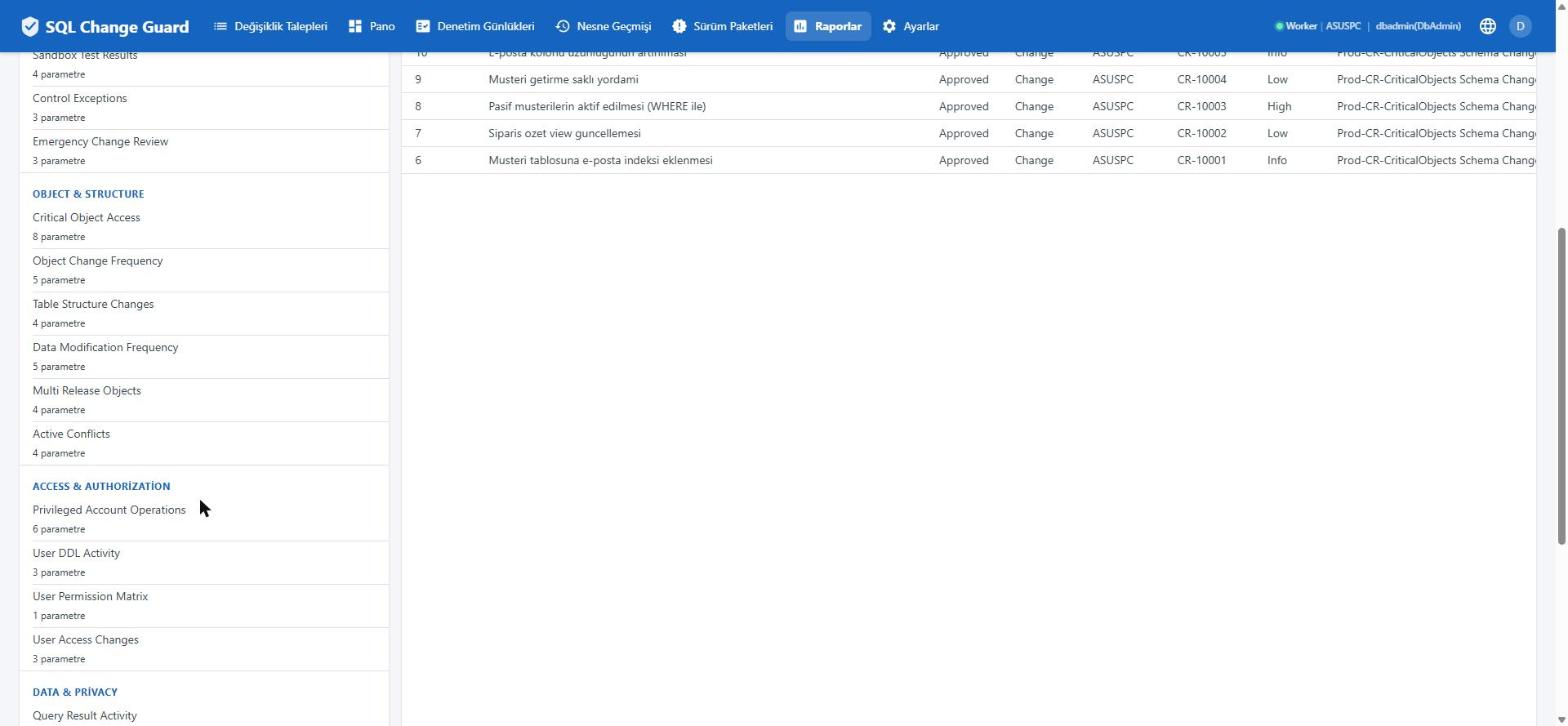
| GrupGroup | Hangi soruyu cevaplarThe question it answers |
|---|---|
| Change Governance | Hangi talep açıldı, ne kadar bekledi, kim onayladı, ne çalıştı, ne reddedildi.Which requests were opened, how long they waited, who approved them, what ran and what was rejected. |
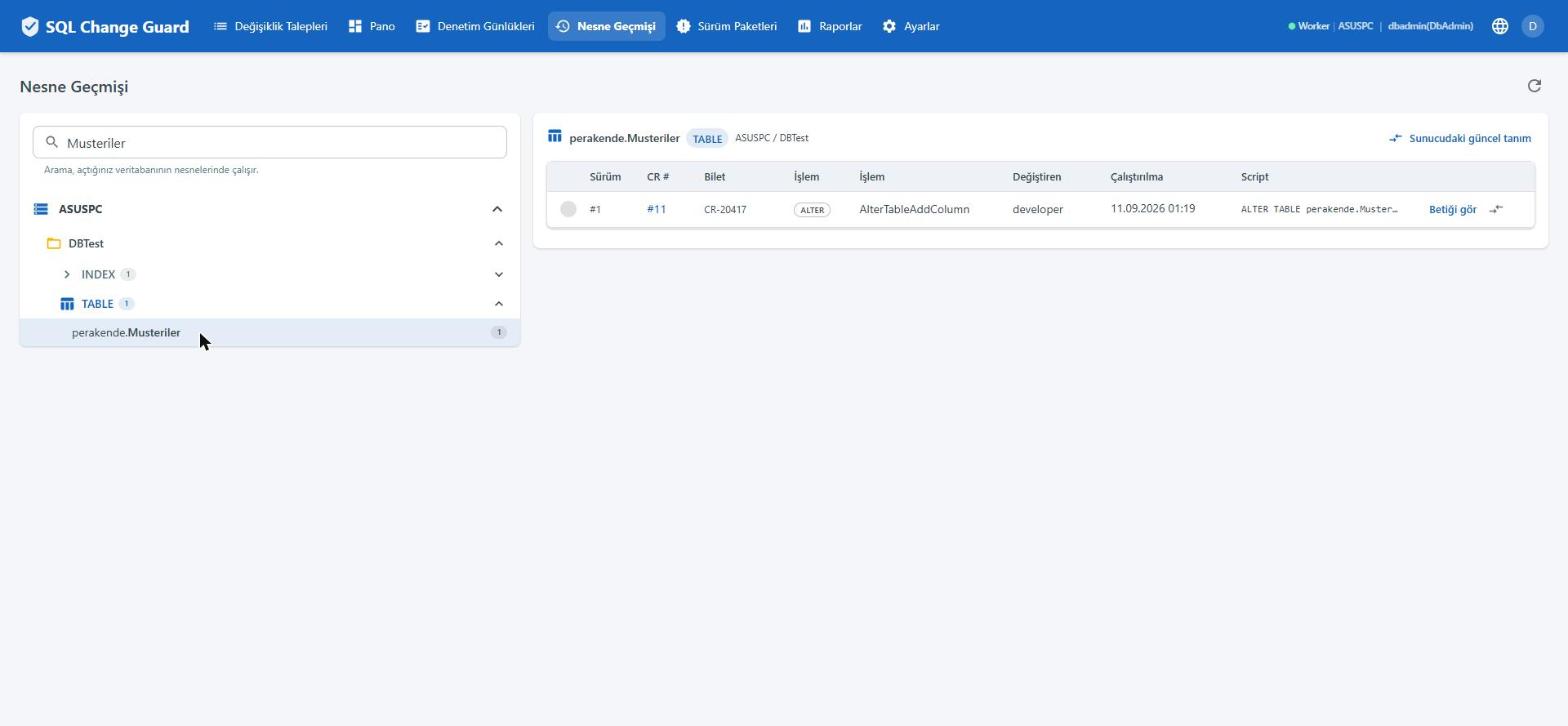
| Object & Structure | Hangi nesneye kim dokundu, hangi nesne ne sıklıkta değişti, nerede çakışma var.Who touched which object, how often each object changes, where the collisions are. |
| Access & Authorization | Kim hesap açtı, kim yetki değiştirdi, ayrıcalıklı hesaplar ne yaptı.Who created accounts, who changed permissions, what privileged accounts did. |
| Data & Privacy | Üretim verisine kim erişti, hangi kolon maskelendi, veriyi doğrudan değiştiren talepler hangileri.Who accessed production data, which columns were masked, which requests modified data directly. |
| Configuration & Compliance | Hangi ayar değişti, hangi kontrol istisnası oluştu, onay izi nasıl ilerledi.Which settings changed, which control exceptions occurred, how the approval trail progressed. |
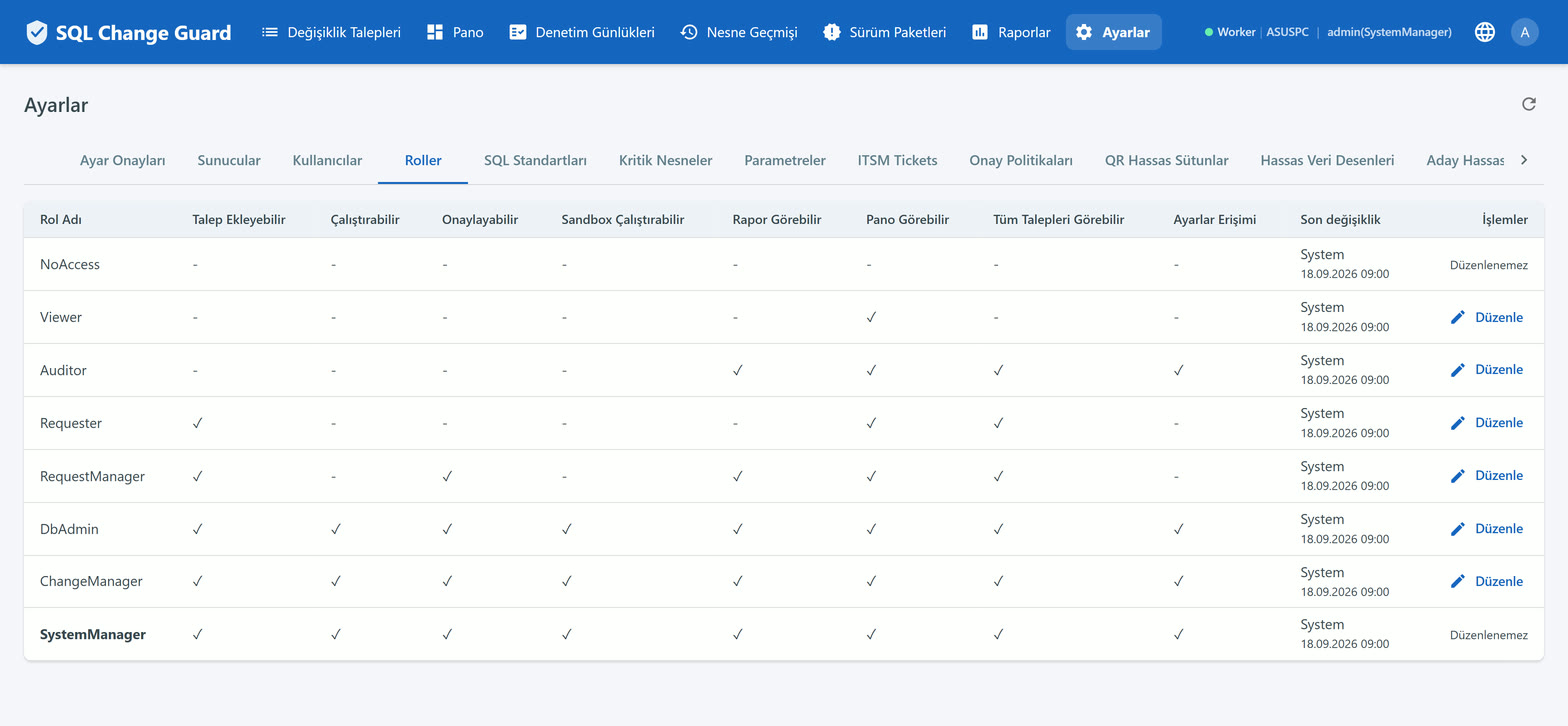
Raporların bir kısmı belirli rollerle sınırlıdır ve bu sınır sunucuda uygulanır; diğerleri rapor görme iznine sahip herkese açıktır. Rapor çıktıları İngilizcedir. Some reports are limited to specific roles and that limit is enforced on the server; the rest are open to everyone with the report view permission. Report output is in English.