Infrastructure Manager

Hangi sunucuda ne değişti, tek yerden okunuyor mu? Can you read what changed on which server in one place?

Ortam sayısı arttıkça sorun kapasite değil, görünürlük oluyor. As the number of environments grows, the problem stops being capacity and becomes visibility.

Bugün bu soru nasıl cevaplanıyorHow this question is answered today

Her sunucunun kendi kaydı var. Bazılarında izleme aracı, bazılarında sistem logu, bazılarında sadece yedek geçmişi.

Every server has its own record. Some have a monitoring tool, some have system logs, some have only a backup history.

"Bu değişiklik hangi sunucuya gitti" sorusunu cevaplamak için birden fazla yere bakmak gerekiyor. Cevap genellikle bulunuyor, ama zaman alıyor.

Answering "which server did this change reach" means looking in several places. The answer is usually found, but it takes time.

Ortamlar zamanla birbirinden ayrışıyor. Test ile üretimin farkı, kimsenin planlamadığı küçük müdahalelerle büyüyor.

Environments drift apart over time. The difference between test and production grows through small interventions nobody planned.

Bu cevabın maliyetiWhat that answer costs

Ortam sapması. Testte çalışan bir değişikliğin üretimde çalışmama sebebi çoğu zaman budur.Environment drift. It is the usual reason a change that worked in test fails in production.
Bir talebin birden fazla sunucuya gitmesi durumunda hangisinde başarılı olduğunun ayrı ayrı takip edilmesi.When one request targets several servers, tracking which of them succeeded one by one.
Bir sunucunun yönetişim kapsamı dışında kalması. Genelde en eski ve en kritik olan sunucudur.One server sitting outside the governance scope. It is usually the oldest and most critical one.
Yetki ve rol değişikliklerinin değişiklik sayılmaması. Kayıtta görünmez, denetimde sorulur.Privilege and role changes not counting as changes. Invisible in the record, asked about in the audit.

Yönetişim bunu nasıl değiştirirWhat governance changes

Sunucu, yönetişimin bir parametresi olur. Sorgu sonucu talebi birden fazla sunucuya gidebilir ve her sunucunun sonucu ayrı kayıtlıdır; değişiklik talebi tek sunucuya gider, çünkü sunucular arasında ortak transaction yoktur.

The server becomes a parameter of governance. A query result request can target several servers and the outcome for each is recorded separately; a change request goes to a single server, because there is no shared transaction across servers.

Kapsam listesi sekiz yolu içerir ve bu listede yetki değişikliği ile bakım işleri de vardır. Bunlar çoğu kurumda kapsam dışıdır.

The scope list covers eight paths, and it includes privilege changes and maintenance work. In most organisations those sit outside scope.

Nesne geçmişi, bir nesneye ürün üzerinden dokunan bütün talepleri gösterir. "Sunucudaki güncel tanım" karşılaştırması ise nesnenin hedefteki o anki halini okur; ürünün dışından yapılmış bir değişiklik bu güncel tanımda okunabilir, ancak ürün bunu kendiliğinden tespit etmez.

Object history shows every request that touched an object through the product. The "current definition on the server" comparison reads the object as it is on the target right now; a change made outside the product can be read in that current definition, but the product does not detect it on its own.

Ürün üzerinden hangi sunucuda neyin değiştiği tek yerden okunur. Ürün yalnız kendisine tanımlı sunucuları bilir; kapsamın tamamlığı, kurumun sunucu envanteriyle ürünün sunucu listesinin karşılaştırılmasıyla gösterilir. What changed on which server through the product is readable in one place. The product only knows the servers defined in it; completeness of scope is shown by comparing the organisation's server inventory with the product's server list.

Yetkinin durduğu iki ekranThe two screens where access lives
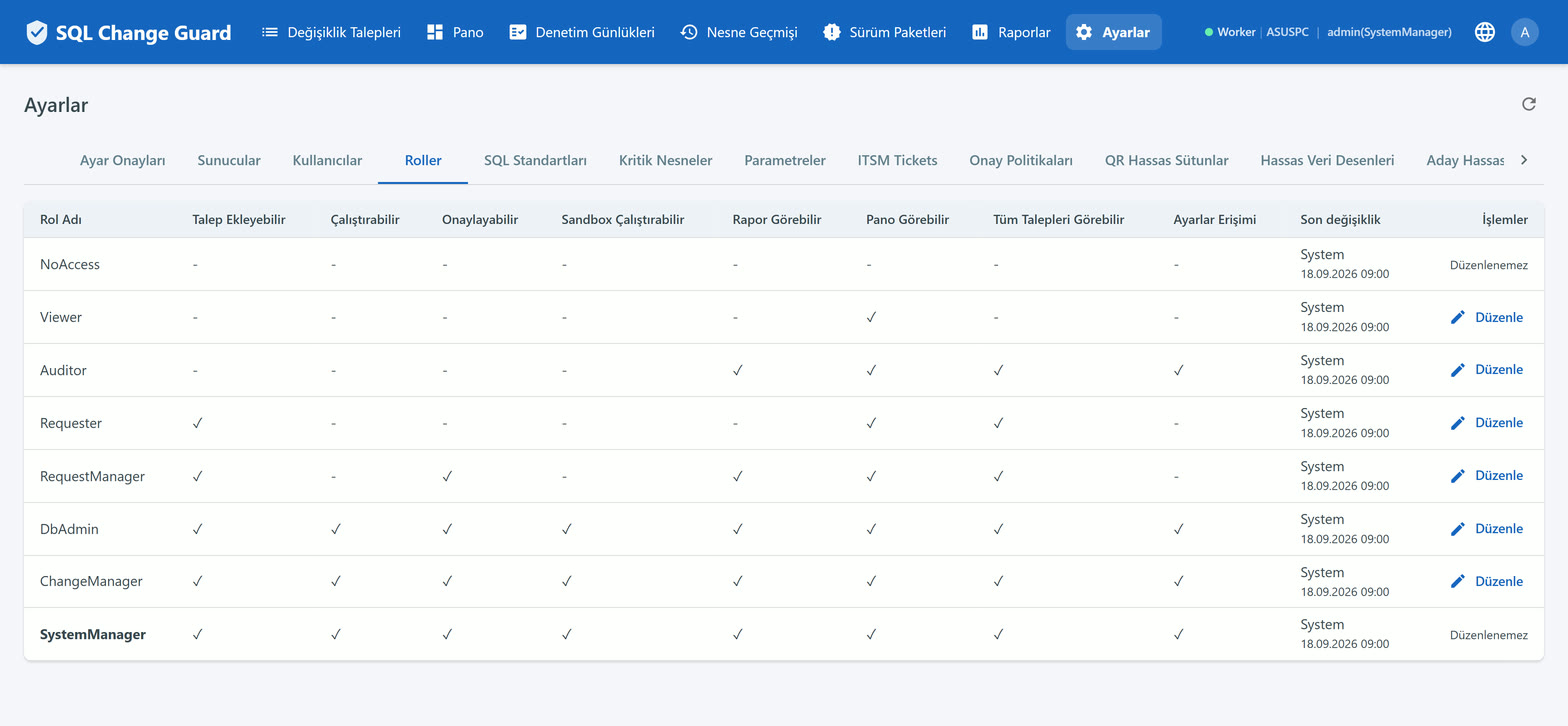
Rol yetkileri ekranı: talep, onay, çalıştırma, görünürlük ve ayar yönetimi yetkilerinin rol bazında açılıp kapatılması
Roller ve yetkilerRoles and permissions Talep açma, onaylama, çalıştırma ve ayar yönetimi rol bazında açılır kapanır. Kontrol arayüzde değil sunucuda uygulanır. Requesting, approving, executing and managing settings are switched per role. The check is enforced on the server rather than in the interface.
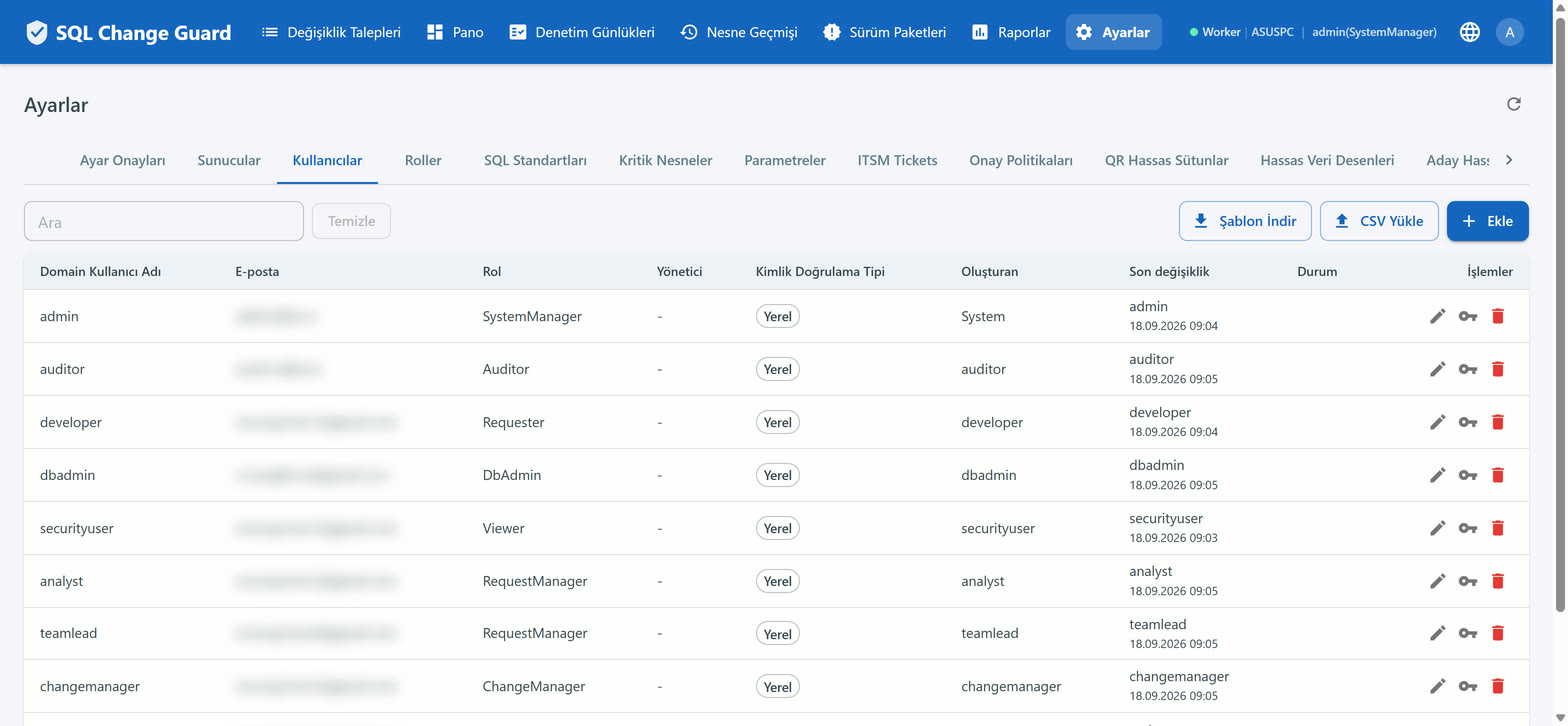
Kullanıcılar ekranı: rol ataması, yerel veya kurumsal dizin ile kimlik doğrulama ve CSV ile toplu kullanıcı aktarımı
Kullanıcılar ve toplu aktarımUsers and bulk import Yerel hesap veya kurumsal dizin. Kurulumda ekibin tamamı CSV ile aktarılır, tek tek eklemeyle aynı kontrollerden geçer. A local account or the corporate directory. At setup the whole team is imported from CSV, through the same checks as adding one by one.